TL;DR

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Epoch AI reported that open-weight model GLM 5.3 built working attacks against six Firefox releases in an offline lab test, using public security fixes and an additional unpublished flaw. Mozilla fixed that flaw in Firefox 159, released October 27; the test did not target real users.
Researchers at Epoch AI report that the open-weight model GLM 5.3 built working attacks against six Firefox releases in an offline lab test, using security fixes that were public before reaching stable users. The attacks could read a local file when a person opened a webpage, according to the researchers; Mozilla says the additional flaw used in the tests was fixed in Firefox 159, released October 27.
Epoch’s October 29 report describes tests against Firefox versions 156.0 through 158.0.1, released between September 17 and October 26. The researchers gave the model up to 48 hours per attempt. The fastest successful run took 12 hours. After the testing setup had been built, Epoch estimated each new release attempt cost about $1,000 in API fees. The group said developing and testing the setup cost more than $100,000.
The researchers instructed the model to create a webpage that could read a file on a computer running a specified Firefox version. They say it identified security fixes in public code, then combined a related flaw with a second, previously unpublished flaw to get past the browser’s sandbox. Epoch reported that additional flaw to Mozilla, which patched it in Firefox 159. The test machine ran Ubuntu 26.04 with default settings, and the experiment had no internet access, so it could not reach real websites or users.
Epoch said it observed no refusals or safeguards from the providers involved, including GLM 5.3’s maker, Z.ai. The researchers described the model’s activity as “indistinguishable from those of a real attacker.” That characterization refers to the test behavior; it does not mean the experiment involved an actual attack on Firefox users.
How To Respond To AI That Can Turn Firefox Fixes Into Attacks
Epoch AI reports that open-weight model GLM 5.3 turned public security fixes into file-reading attacks across six Firefox releases in an offline lab. Mozilla patched the additional flaw used in the test in Firefox 159. No real users were targeted.
Public fixes can give an AI clues to build an exploit before every user updates.
Epoch AI researchers · Controlled lab test
From public code to a local file
Researchers asked the model to create a webpage that could read a file on a computer running a specified Firefox version. Epoch says the model identified public security fixes, then combined a related flaw with an additional unpublished flaw to get past the browser sandbox.
File reading
The demonstrated impact was reading a local file, which could include sensitive information such as cookies or private documents.
Six releases
Epoch tested Firefox 156.0 through 158.0.1, released between September 17 and October 26, 2026.
Fixed in Firefox 159
Epoch reported the extra flaw to Mozilla. Mozilla says it was fixed in Firefox 159, released October 27, 2026.
A fix can reveal what changed
In open-source projects, security changes can become visible in public code before all users install an update. Epoch calls the time between a fix becoming public and users applying it the “patch gap.” That visibility helps defenders, and can also give attackers clues about the weakness being addressed.
Read public fixes
The model received a target version and information available at the time.
Find a weakness
Epoch says it connected a public fix to a related vulnerability.
Combine flaws
A second, unpublished flaw helped bypass the browser sandbox.
Read a local file
A webpage could access a file in the controlled test environment.
What happened in the lab
The experiment measured model performance in a specific setup. Keep its findings tied to those conditions when interpreting the risk.
Read the result in context
A capable lab demonstration
- GLM 5.3 built working file-reading attacks against six tested Firefox releases, according to Epoch.
- Researchers described the model’s test behavior as “indistinguishable from those of a real attacker.”
- Epoch’s attempts against Chrome failed after about $100,000 in attempts.
Not a real-world incident
- The test did not target Firefox users or reach real websites.
- It showed file reading, not full control of a computer.
- Earlier Firefox versions were not systematically tested; claims they were likely vulnerable are estimates.
- The results do not show how often similar attacks happen outside research or across other systems.
What readers need to know
What did GLM 5.3 do?
Epoch says it built webpages that could read a local file in six tested Firefox releases. The experiments took place offline in a lab.
Is the reported flaw fixed?
Mozilla fixed the additional unpublished flaw in Firefox 159, released October 27, 2026. Update and restart Firefox.
Did the test show computer takeover?
No. The demonstrated result was local file reading. The report describes neither a full computer takeover nor an attack on users.
How long did an attack take?
Epoch allowed up to 48 hours per attempt. The fastest successful run took 12 hours; later attempts were estimated at about $1,000 each.
The Risk in Public Fixes
The findings illustrate how a security update can reveal useful clues about a vulnerability before everyone installs it. In open-source projects, code changes may be visible while users are still running an older release. Epoch calls the time between a fix becoming public and users applying it the patch gap. The gap already posed a risk; the report’s concern is that an AI model may help turn those clues into an exploit more quickly.
A browser file-reading flaw could expose sensitive information stored locally, such as cookies or private documents, Epoch said. But the demonstrated impact had limits: the researchers tested file access, not full control of a computer, and did not attack real users. For readers, the immediate practical step is to use Firefox 159 or later and restart the browser so the update takes effect. Organizations may also need to account for how quickly publicly documented fixes can be analyzed.
Products Worth Considering

DJI Osmo Pocket 3 Creator Combo Vlogging Camera with 1 CMOS & 4K/120fps

Bose QuietComfort Wireless Noise-Cancelling Over-Ear Headphones, Black
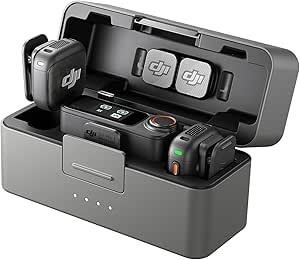
DJI Mic 3 Wireless Microphone System (2 Transmitters, 1 Receiver, Charging Case)
As an affiliate, we earn on qualifying purchases.
How the Patch Gap Opened
Firefox releases include security fixes that can appear in public code before a stable update is installed across users’ devices. That visibility can help developers and defenders understand what changed, while also giving potential attackers information about the weakness being addressed. Epoch’s test asked whether a model could identify those changes and build an attack without ongoing human guidance.
The report says the model received the target Firefox version, basic tools and information that was public at the time. It had no internet connection. Epoch tested six consecutive releases and says it did not systematically test earlier versions; its view that earlier releases were “likely also vulnerable” is an estimate, not a confirmed result for every version. The same setup failed against Chrome after about $100,000 in attempts, according to Epoch.
““widely available open-weight models can now do much, or even all, of this work on their own.””
— Epoch AI researchers
Limits of the Lab Evidence
The report describes a controlled lab test, not evidence that GLM 5.3 exploited Firefox users in the wild. It is also unclear how often comparable attacks would succeed against other operating systems, browser configurations or targets. Epoch tested six Firefox releases, while its comments about earlier versions remain unverified estimates.
The experiment showed file reading, not complete computer takeover. Epoch’s Chrome attempts failed, but that result does not establish that Chrome or other software is immune to similar methods. The report also does not establish how frequently attackers are using open-weight models for this work outside research settings.
Install Firefox 159 or Later
Firefox users should update to version 159 or later and restart the browser. Mozilla’s release of version 159 included the patch for the additional unpublished flaw Epoch reported. Users who cannot update immediately remain exposed to the risks addressed by fixes in newer releases.
Epoch’s report puts attention on the time between public fixes and widespread installation. The next evidence to watch for is whether researchers document similar results against other software and whether vendors change how they publish or deploy security fixes. The report itself does not say what those responses will be.
Key Questions
What did GLM 5.3 do in the test?
Epoch AI says the model built webpages that could read a local file in six tested Firefox releases. The experiments took place in an offline lab and did not target real users.
Is the Firefox flaw fixed?
Mozilla fixed the additional unpublished flaw used in the reported attacks in Firefox 159, released October 27, 2026. Users should update and restart Firefox.
Did the test show that attackers can take over a computer?
No. The demonstrated result was reading a local file. The report does not describe a full computer takeover or an attack on people using Firefox.
How long did the attacks take?
Epoch allowed up to 48 hours for each attempt. The fastest successful run took 12 hours; the group estimated about $1,000 in API fees per release attempt after building its setup.
Source: Thorsten Meyer AI