TL;DR

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Europe has invested over €2 billion in sovereign cloud initiatives to reduce US legal exposure. However, most data centers still rely on Intel and AMD processors, which contain management engines that pose security risks. Experts warn these embedded chips could be exploited as backdoors, undermining sovereignty efforts.
European efforts to establish sovereign cloud infrastructure are underway, funded by over €2 billion through initiatives like the EU’s IPCEI-CIS program, but reliance on US-made processors with embedded management engines creates significant security vulnerabilities.
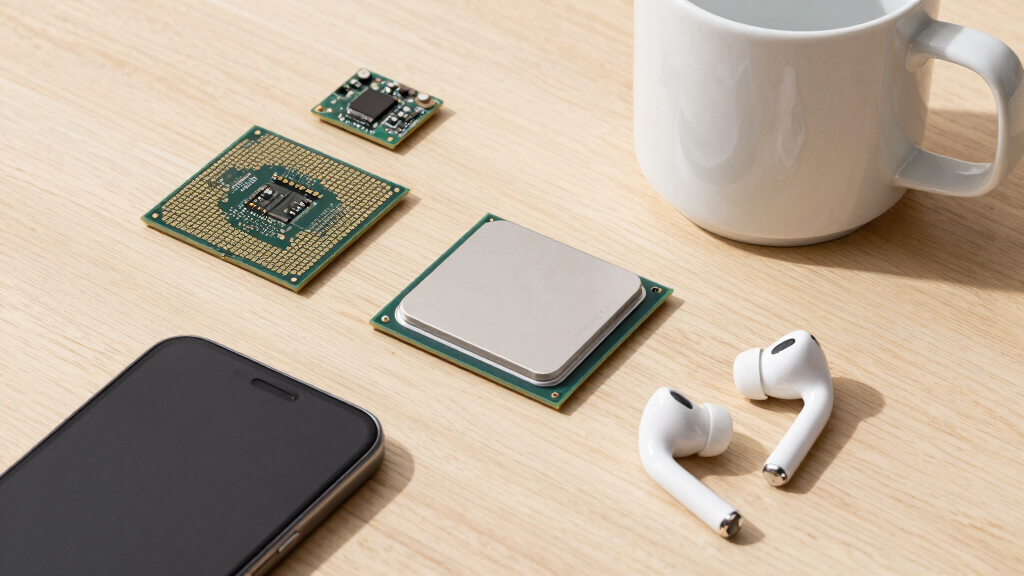
Most European data centers and qualified cloud operators continue to depend heavily on Intel and AMD processors. Inside these chips are management engines—Intel’s Management Engine (ME) and AMD’s Platform Security Processor (PSP)—which operate at a privilege level below the operating system, outside its control. These management engines have their own memory, network stacks, and can generate traffic indistinguishable from host traffic, posing a security risk.
Security researchers, including John Goodacre, have described these engines as “a computer inside your computer,” capable of persistent activity even when devices appear powered off. Exploits leveraging these management engines have been documented, including covert exfiltration channels used by nation-state actors, and vulnerabilities demonstrated in recent academic research, such as the Fabricked attack on AMD’s SEV-SNP technology.
European frameworks like SecNumCloud certify cloud operators based on security standards but do not assess the silicon-level security of processors. This gap leaves a vulnerability that could be exploited by malicious actors, undermining the goal of digital sovereignty.
Why It Matters
This development is significant because it exposes a critical weakness in Europe’s strategy to achieve digital sovereignty. Despite investing heavily in infrastructure, reliance on US processors with embedded management engines means that sovereignty could be compromised through hardware backdoors. This has implications for national security, data privacy, and the integrity of European cloud services.
Products Worth Considering

Apple MacBook Air 15-inch with M5 chip, 24GB RAM, 512GB SSD, Midnight

Apple MacBook Air 13.6-inch with M5 Chip, 16GB Memory, 512GB SSD, Sky Blue

LG UltraGear 32GX850A-B 32-inch 4K UHD Glossy OLED Gaming Monitor
As an affiliate, we earn on qualifying purchases.
Background
European countries and the EU have prioritized reducing dependence on US technology, with initiatives like IPCEI-CIS funding infrastructure and certifying cloud providers under frameworks like SecNumCloud. However, the hardware layer—specifically the silicon chips—remains largely unaddressed, with most processors still containing management engines susceptible to exploitation. Past incidents, such as the NSA’s use of covert channels and recent academic demonstrations of vulnerabilities, highlight the persistent risks at this layer.
“It’s a computer inside your computer. The management engine has its own memory, its own clock, and its own network stack, operating independently of the host.”
— John Goodacre, Professor of Computer Architectures
“Yes, it can probably be used as a backdoor, like many other firmware components. The real question is whether operational controls can make it unreachable in practice.”
— Professor Aurélien Francillon, security researcher at EURECOM
What Remains Unclear
It remains unclear how widespread or easily exploitable these vulnerabilities are in current European data centers, as many operators have not yet conducted silicon-level security assessments. The extent to which these management engines could be exploited in real-world attacks on sovereign clouds is still under investigation.
What’s Next
European policymakers and cloud providers are expected to evaluate hardware security more thoroughly, potentially developing standards to certify processors without vulnerable management engines. Further research and collaboration are likely to focus on designing chips that support sovereign control at the silicon level.
Key Questions
Why are management engines in processors a security concern?
Management engines operate at a privilege level below the operating system, with independent memory and network access. They can be exploited as backdoors, allowing malicious actors to access or exfiltrate data without detection.
Are European cloud providers aware of these vulnerabilities?
While European frameworks certify cloud providers based on security standards, they do not currently assess the security of the silicon chips themselves, leaving a potential gap in hardware-level security.
Can these vulnerabilities be fixed through software updates?
Many vulnerabilities stem from hardware design features, which are difficult to patch through software alone. Addressing them requires hardware redesigns or using processors without vulnerable management engines.
What steps are European governments taking to address this issue?
Most efforts are focused on policy and certification frameworks at the software and infrastructure level, with ongoing discussions about hardware security standards and the development of sovereign processors.