
TL;DR
Microsoft’s November 10, 2026, Patch Tuesday release notes list 1,094 Microsoft CVEs, following 1,474 in October. One Outlook flaw was exploited before its fix; a separate Paint fix has had version and availability issues. Microsoft has said AI contributes to vulnerability discovery but has not disclosed how many November fixes came from AI.
Microsoft’s November 10, 2026, Patch Tuesday release lists 1,094 Microsoft CVEs, including a fix for an Outlook vulnerability that was exploited before a patch was available. The release follows an even larger October batch of 1,474 fixes, while a separate Paint vulnerability has drawn attention because the initially identified fixed version reportedly remained vulnerable and the corrected version may not yet be available to all users.

Get the latest gadgets delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Microsoft’s Security Update Guide release notes say the November release consists of 1,094 Microsoft CVEs. Krebs on Security counted 1,093 published on November 10; the one-item difference is CVE-2026-109469, a Critical Entra Device Registration flaw published five days earlier. Microsoft says no customer action is needed for that flaw. The source’s tally of Microsoft entries excludes flaws attributed to other vendors that Microsoft also republishes.
The Outlook issue, CVE-2026-124194, can expose a user’s NTLMv2 password hash when a crafted file is opened, according to the source material. The Cybersecurity and Infrastructure Security Agency added it to its catalog of exploited vulnerabilities on November 10. Administrators should prioritize the Outlook and Office updates, then review the Critical server flaws relevant to their environments.
A separate Paint flaw, CVE-2026-83844, was published October 13. Heise reported that the version Microsoft initially identified as fixed remained vulnerable. The corrected version, 11.2609.401.0, was identified November 6, but PC Gamer reported it was not appearing for some users. The source advises checking Paint separately through the Microsoft Store.
Patch Volume and Admin Priorities
The scale of the release makes triage more demanding for organizations that need to test and deploy updates across many products. The source material lists 726 Windows CVEs and 174 Office CVEs, alongside fixes for SQL Server, developer tools, SharePoint Server, Azure, Exchange Server and Defender. Those product totals help explain why teams may need to prioritize based on exposure and system role rather than treating every fix as equally urgent.
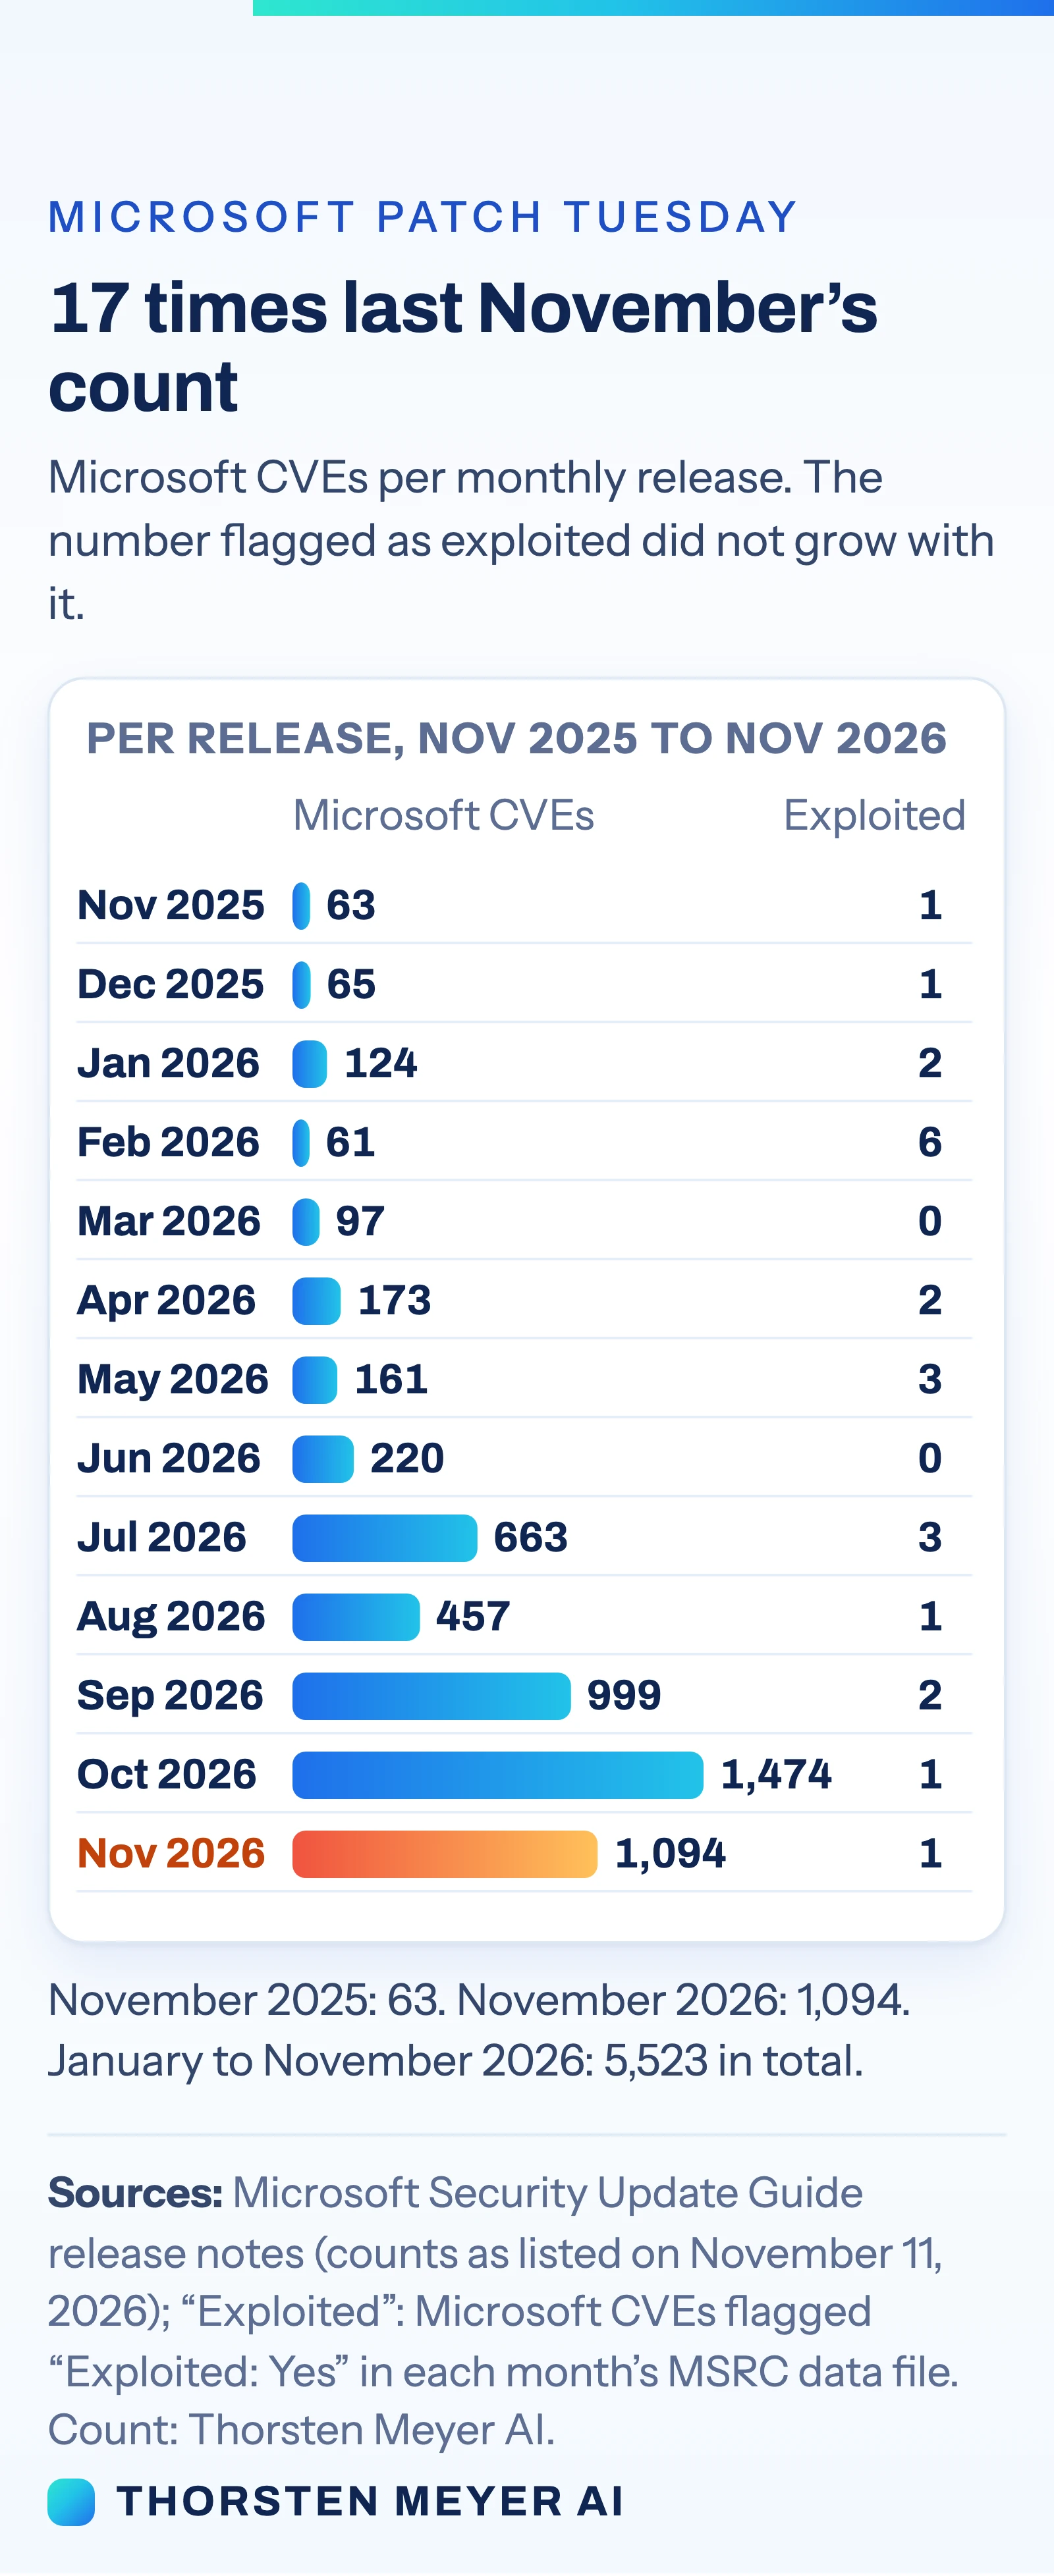
The count alone does not show that attackers have exploited a comparable number of flaws. The source’s review of Microsoft’s monthly data files found between zero and six entries marked as exploited per month; November had one such flaw. That distinction matters: the large release raises patch-management workload, while the Outlook issue provides a specific reason for prompt attention.
Paint’s reported version problem also shows why deployment status matters after a fix is announced. A release note or version number may not mean every user has received the update, so administrators and individuals may need to confirm the installed version through the relevant distribution channel.
Products Worth Considering

Apple Watch Series 12 GPS 42mm Smartwatch

Bose TV Speaker Compact Soundbar with Bluetooth and HDMI-ARC, Black

DJI Mini 4 Pro Fly More Combo with DJI RC 2
As an affiliate, we earn on qualifying purchases.
A Year of Larger Releases
Microsoft’s release notes listed 63 CVEs in November 2025 and 65 in December. The source’s month-by-month review shows the count rising during 2026: 220 in June, 663 in July, 999 in September and 1,474 in October. November’s 1,094 is lower than October’s total but much higher than the same month a year earlier. The source calculates that January through November 2026 added up to 5,523 Microsoft CVEs; Krebs reported more than 5,100 security patches so far, using a different counting method.
Microsoft has previously linked larger releases in part to changes in vulnerability discovery. In an April post, Tom Gallagher, a vice president of engineering at the Microsoft Security Response Center, said AI can help discover more issues across a broader surface. In May, he wrote that advanced AI models are “part of the discovery picture,” while also naming more mature automation and broader outside-researcher participation as factors. Microsoft said releases could continue trending larger for some time and that it was not changing its standard for what qualifies as a bug.
The November data does not establish how much AI contributed to the release. According to the source’s review, 24 November CVE entries credited researchers who used an AI model: 23 cited GLM from z.ai and one cited Claude. Those public credit lines do not reveal Microsoft’s internal tools or the share of findings attributable to AI.
“This release consists of 1094 Microsoft CVEs.”
— Microsoft Security Update Guide
Microsoft has not said how many of the November vulnerabilities were found through its internal use of AI. Public researcher credit lines cover only a subset of entries and do not indicate the tools Microsoft used itself. The release count also differs slightly between Microsoft’s dated release notes and Krebs on Security’s count because one CVE was published earlier.
For Paint, the source reports that the corrected version is 11.2609.401.0, but some users may not see it in the Microsoft Store. The available material does not establish how widespread the availability issue is or whether every affected installation has received the correction. It also does not provide details on the other Critical server flaws beyond their product categories and count.
Verify and Deploy the Fixes
Microsoft customers should review the November Security Update Guide and apply relevant updates, giving priority to the Outlook and Office fixes and to Critical server vulnerabilities affecting their systems. They should confirm deployment rather than relying solely on the release announcement, especially for systems exposed to the Outlook issue.
Paint users can check for version 11.2609.401.0 through the Microsoft Store and confirm whether the update is installed. Further reporting or Microsoft guidance may clarify the rollout’s reach. Microsoft’s subsequent monthly release notes will show whether the high CVE counts continue, but the November material does not provide a date or forecast for the next release’s total.
Key Questions
How many CVEs did Microsoft list in its November 2026 release?
Microsoft’s November 10 release notes list 1,094 Microsoft CVEs. Krebs on Security counted 1,093 published that day; the difference is a flaw published on November 5.
Which November flaw was reported as exploited?
CVE-2026-124194 affects Outlook. According to the source material, opening a crafted file can expose a user’s NTLMv2 password hash. CISA added the flaw to its exploited-vulnerabilities catalog on November 10.
What is the issue with the Paint patch?
The source says the version Microsoft initially named as fixed for CVE-2026-83844 remained vulnerable, according to heise. Version 11.2609.401.0 was identified as the working version on November 6, but PC Gamer reported that some users still could not see it.
Did AI account for the large number of November fixes?
Microsoft has said AI is one part of its vulnerability-discovery process, alongside automation and outside research. It has not disclosed how many November fixes came from AI. The source identified 24 November CVE credit lines referring to researchers using AI models, which does not show Microsoft’s internal contribution.
Source: Thorsten Meyer AI