📊 Full opportunity report: Cybersecurity operations signal monitor: A backdoor in a LinkedIn job offer on IdeaNavigator AI — validation score, market gap, and execution plan.

Get the latest gadgets delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
TL;DR
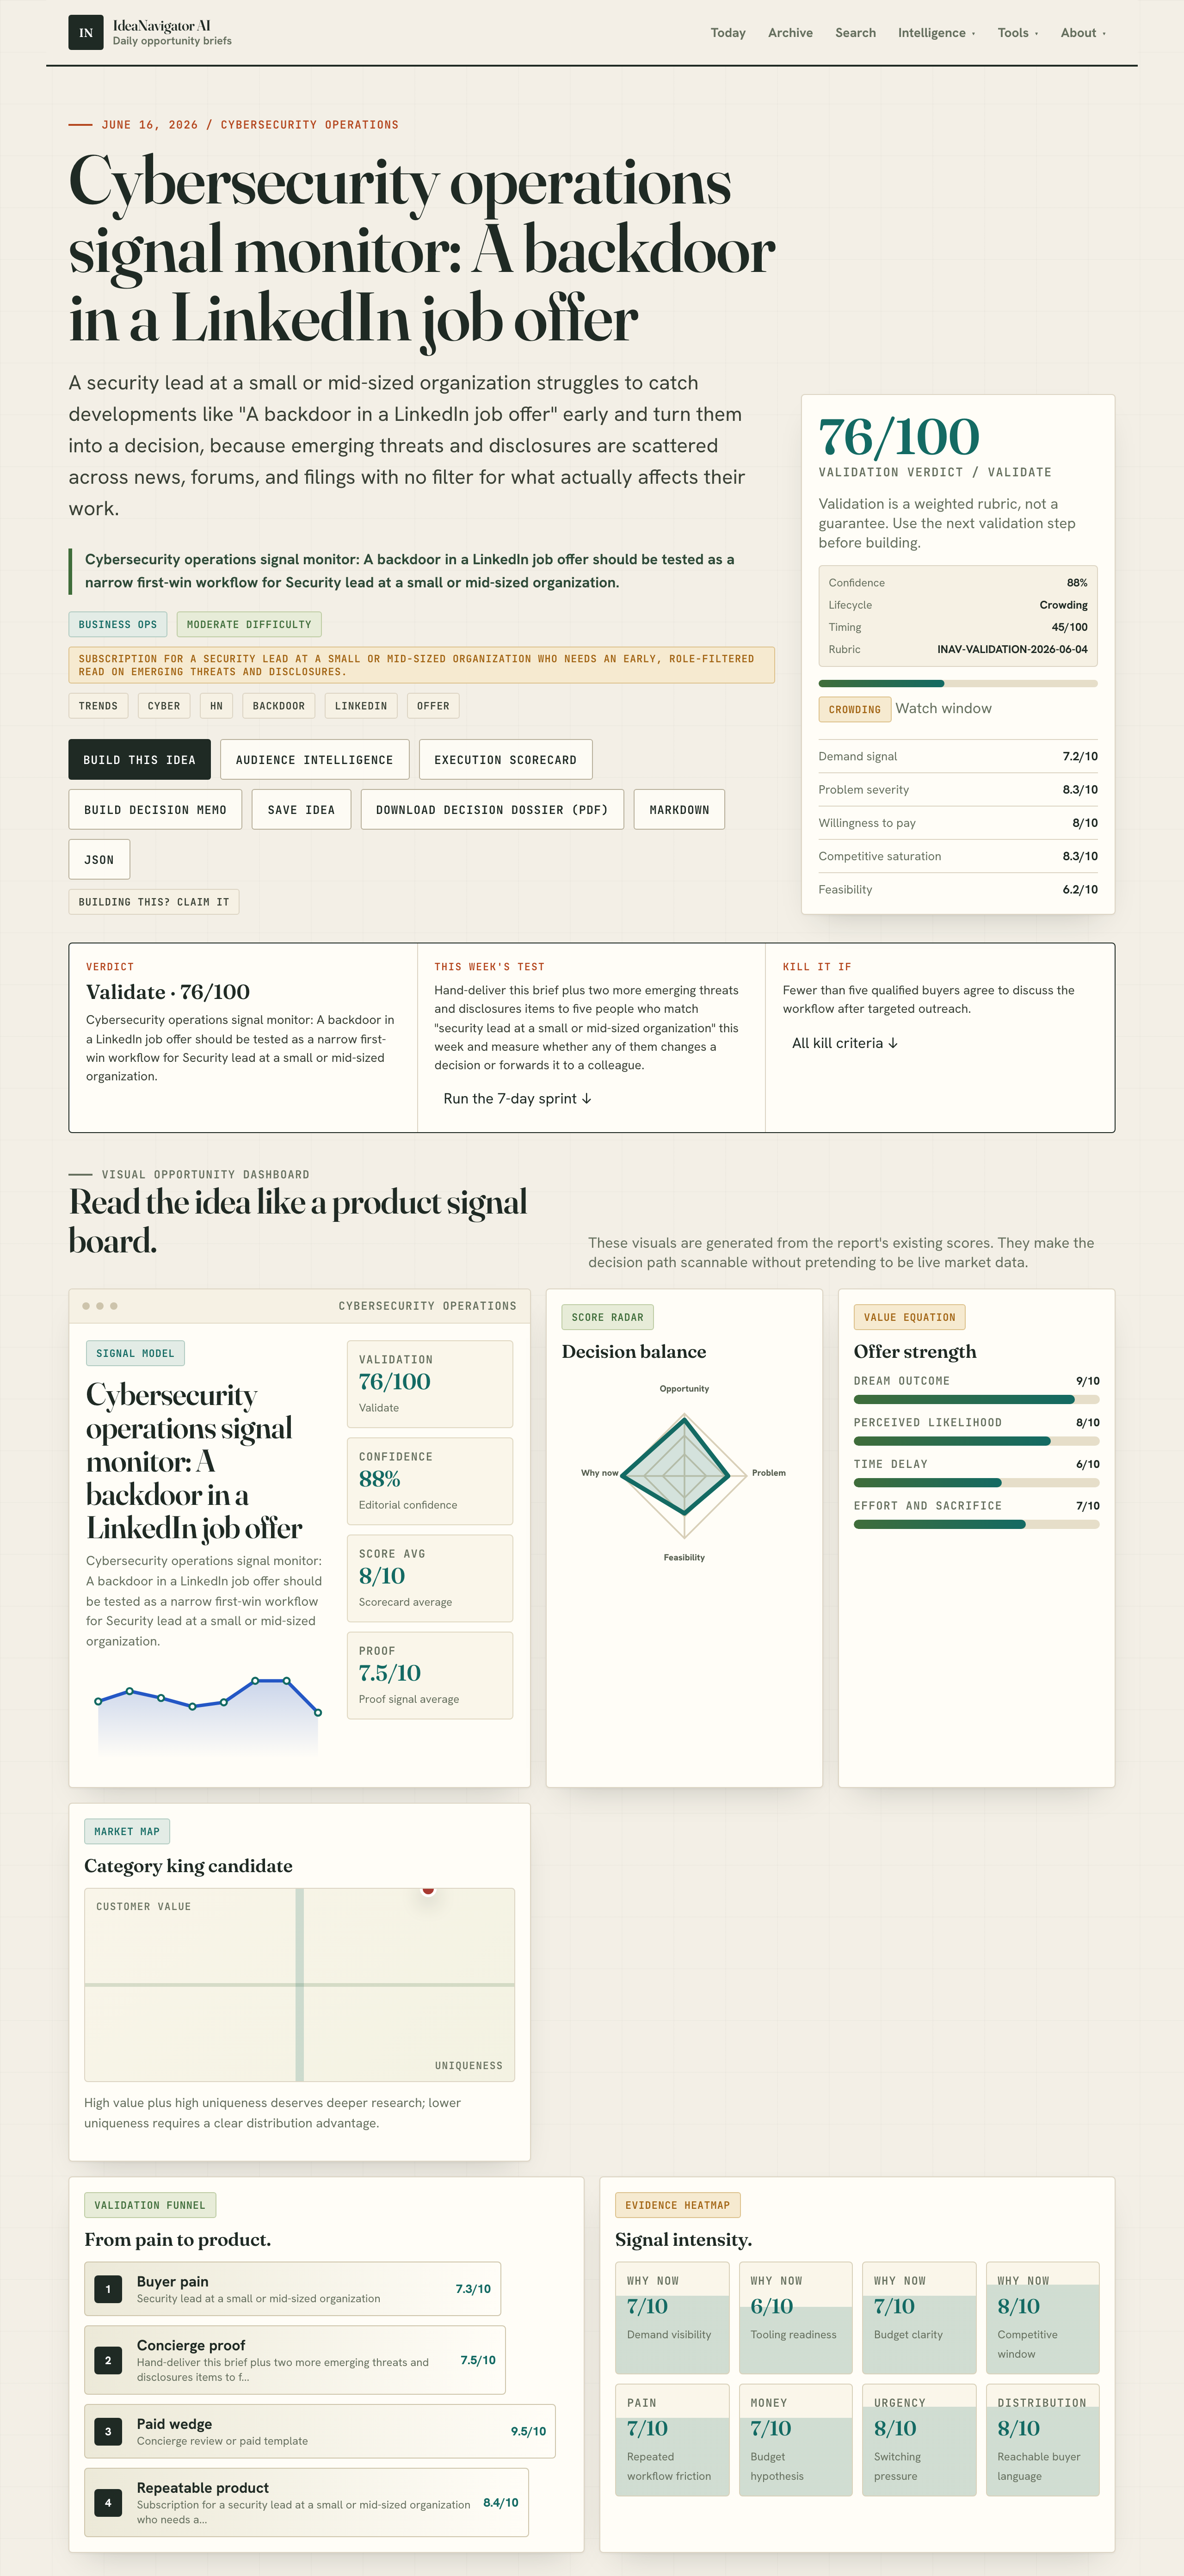
Cybersecurity analysts detected a backdoor embedded in a LinkedIn job offer. This development underscores the importance of role-specific threat monitoring for small and mid-sized organizations. The full impact and scope are still being evaluated.
Cybersecurity analysts have confirmed the discovery of a backdoor embedded within a LinkedIn job posting, marking a significant development in emerging threat tactics targeting organizations of all sizes.
The backdoor was identified by cybersecurity researchers during routine monitoring of online threat signals. It was embedded in a job offer posted on LinkedIn, a platform widely used for professional recruitment. The specific technical details of the backdoor are still under analysis, but initial assessments suggest it could allow unauthorized access to the employer’s network if exploited.
Sources involved in the investigation have not yet disclosed the exact nature of the malicious code or how widespread this tactic might be. Experts emphasize that such backdoors can be used for espionage, data theft, or further malware deployment, making the threat potentially serious for organizations relying on LinkedIn for recruitment.
Implications for Small and Mid-Sized Organizations
This discovery highlights a new attack vector that could be exploited by malicious actors to infiltrate organizations during the hiring process. Small and mid-sized organizations, which often lack extensive cybersecurity defenses, may be particularly vulnerable. The incident underscores the importance of role-specific threat monitoring and the need for organizations to scrutinize online job postings for signs of compromise.
cybersecurity threat detection software
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Emerging Threats in Cybersecurity Recruitment Channels
Recent years have seen a rise in cyber threats targeting recruitment platforms and online job postings. Attackers often embed malicious code in seemingly legitimate postings to gain initial access to corporate networks. This incident follows other reported cases where cybercriminals exploited online job offers to deliver malware or backdoors, emphasizing the evolving tactics used by threat actors.
Cybersecurity firms and researchers have increasingly called for enhanced monitoring of online signals, especially on platforms like LinkedIn, which serve as critical vectors for initial compromise in targeted attacks.
“The backdoor embedded in this LinkedIn job offer represents a new frontier in targeted attacks. Organizations need to be vigilant when scrutinizing online recruitment postings.”
— an anonymous cybersecurity researcher
network monitoring tools for small business
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Scope and Exploitation of the Backdoor Still Unclear
It is not yet confirmed how widely this backdoor has been used or exploited, nor whether other similar malicious postings are active. The technical specifics are still under investigation, and it remains unclear if this is an isolated case or part of a broader campaign.
cyber threat intelligence platform
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Ongoing Investigation and Development of Monitoring Tools
Security teams are actively analyzing the backdoor’s technical details and assessing potential impacts. Industry experts recommend that organizations strengthen their online threat detection capabilities and review their recruitment-related cybersecurity protocols. Future updates are expected as more information becomes available, and security vendors may develop targeted detection tools for similar threats.
online job posting security scanner
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How can organizations detect if a job offer is malicious?
Organizations should scrutinize job postings for unusual language, verify the legitimacy of the posting source, and monitor network activity for any signs of compromise linked to online recruitment channels.
What steps should companies take after discovering a backdoor in a job posting?
Immediately review and isolate affected systems, conduct a thorough investigation, notify relevant cybersecurity authorities if necessary, and implement enhanced monitoring of online recruitment activities.
Is this threat limited to LinkedIn or other platforms as well?
While this incident involved a LinkedIn posting, similar tactics could potentially target other online recruitment platforms. Organizations should adopt a broad online threat monitoring strategy.
Are there tools available to detect backdoors embedded in online postings?
Currently, specific tools for detecting malicious code in online job offers are limited, but cybersecurity firms are developing targeted detection solutions, and general threat monitoring practices can help identify suspicious activity.
Source: IdeaNavigator AI
Evergreen bestsellers Picks
bestsellers
As an affiliate, we earn on qualifying purchases.